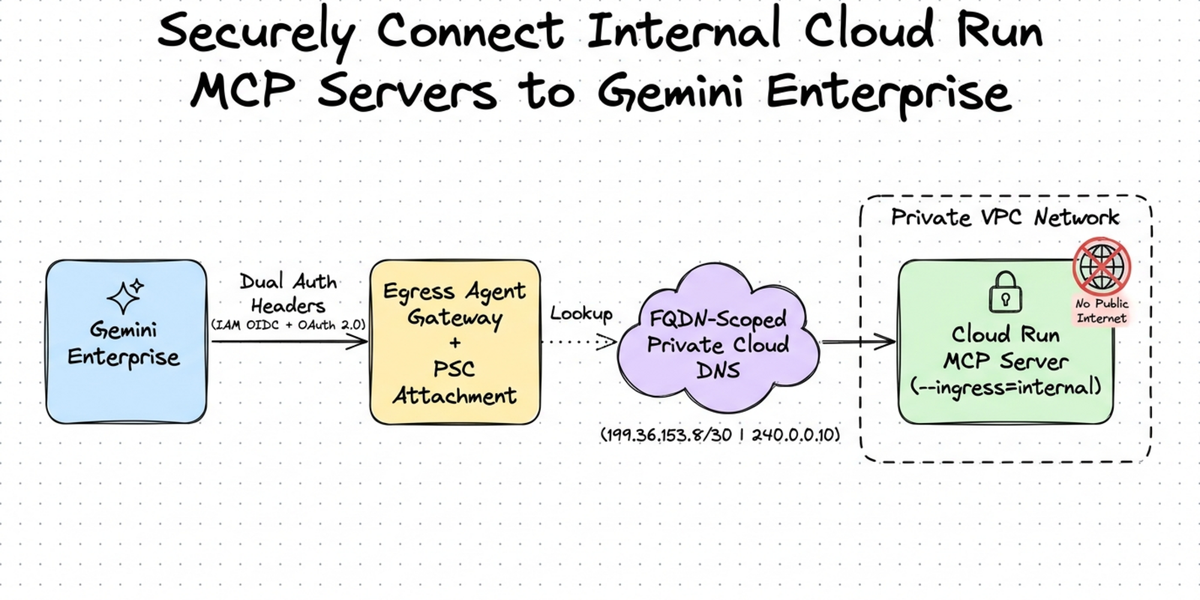
This architecture connects internal Cloud Run MCP servers to Gemini Enterprise using Private Service Connect and FQDN-scoped Private Cloud DNS. It bridges the network gap by resolving hostnames to private VIPs, ensuring traffic stays within your VPC instead of hitting the public internet. A companion GitHub repository provides scripts to automate the deployment of these networking and identity components.
Worth trying if you are running custom MCP servers that must stay off the public internet. The complexity lies in managing the dual authorization headers and precise DNS peering, which adds significant configuration overhead. Not suitable for simple prototypes where public endpoints are acceptable, or teams without experience in advanced GCP networking.
my other side: ivo.blogspot.com


Leave a Reply