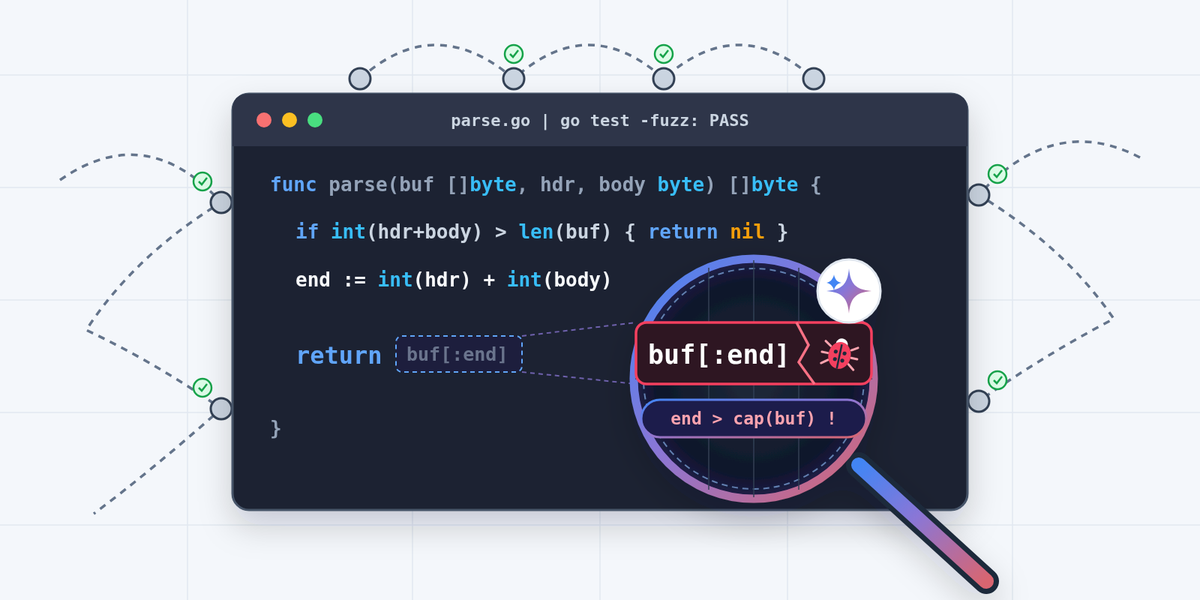
A workflow that compiles Go functions for Linux/RISC‑V, runs Gemini 4 Argon to translate surviving bounds‑check traps into Z3 constraints, and uses Z3 to generate concrete crash inputs. It surfaced three seeded bugs and three hidden bugs in a production Go linter in about a minute per function. The pipeline replaces ad‑hoc fuzzing and manual assembly analysis with a quick, reproducible bug‑hunt.
It’s worth trying if you run a large Go codebase where fuzzing misses edge cases and you can afford a minute per function. The method relies on the LLM’s translation quality and doesn’t provide a formal proof, so it’s not a drop‑in replacement for full verification. It’s best suited for developers comfortable with command‑line tooling and willing to review generated Z3 scripts.
my other side: ivo.blogspot.com


Leave a Reply