Awesome Reverse Engineering tools and frameworks list

15 10 2026
Awesome Reverse Engineering tools and frameworks list

Awesome Reverse Engineering is a curated GitHub repository organizing tools, frameworks, and learning resources by specific tasks like triage, native analysis, and instrumentation. Entries are grouped by objective, such as debugging or unpacking managed code, with commercial options explicitly marked. It provides a structured index that connects practitioners directly to relevant software without wading through generic search results.

It is worth bookmarking if you occasionally need to inspect binaries or unpack proprietary runtimes and want a vetted starting point. However, it is just a directory rather than a tutorial, so you still need to know what questions to ask the tools it lists. Skip it if you are looking for an all-in-one suite or expect hand-holding through your first disassembly session.

more: https://github.com/morluto/awesome-reverse-engineering

my other side: ivo.blogspot.com


ARTEX 한국어판 자율 LLM 침투 테스트 프레임워크

8 10 2026
ARTEX 한국어판 자율 LLM 침투 테스트 프레임워크

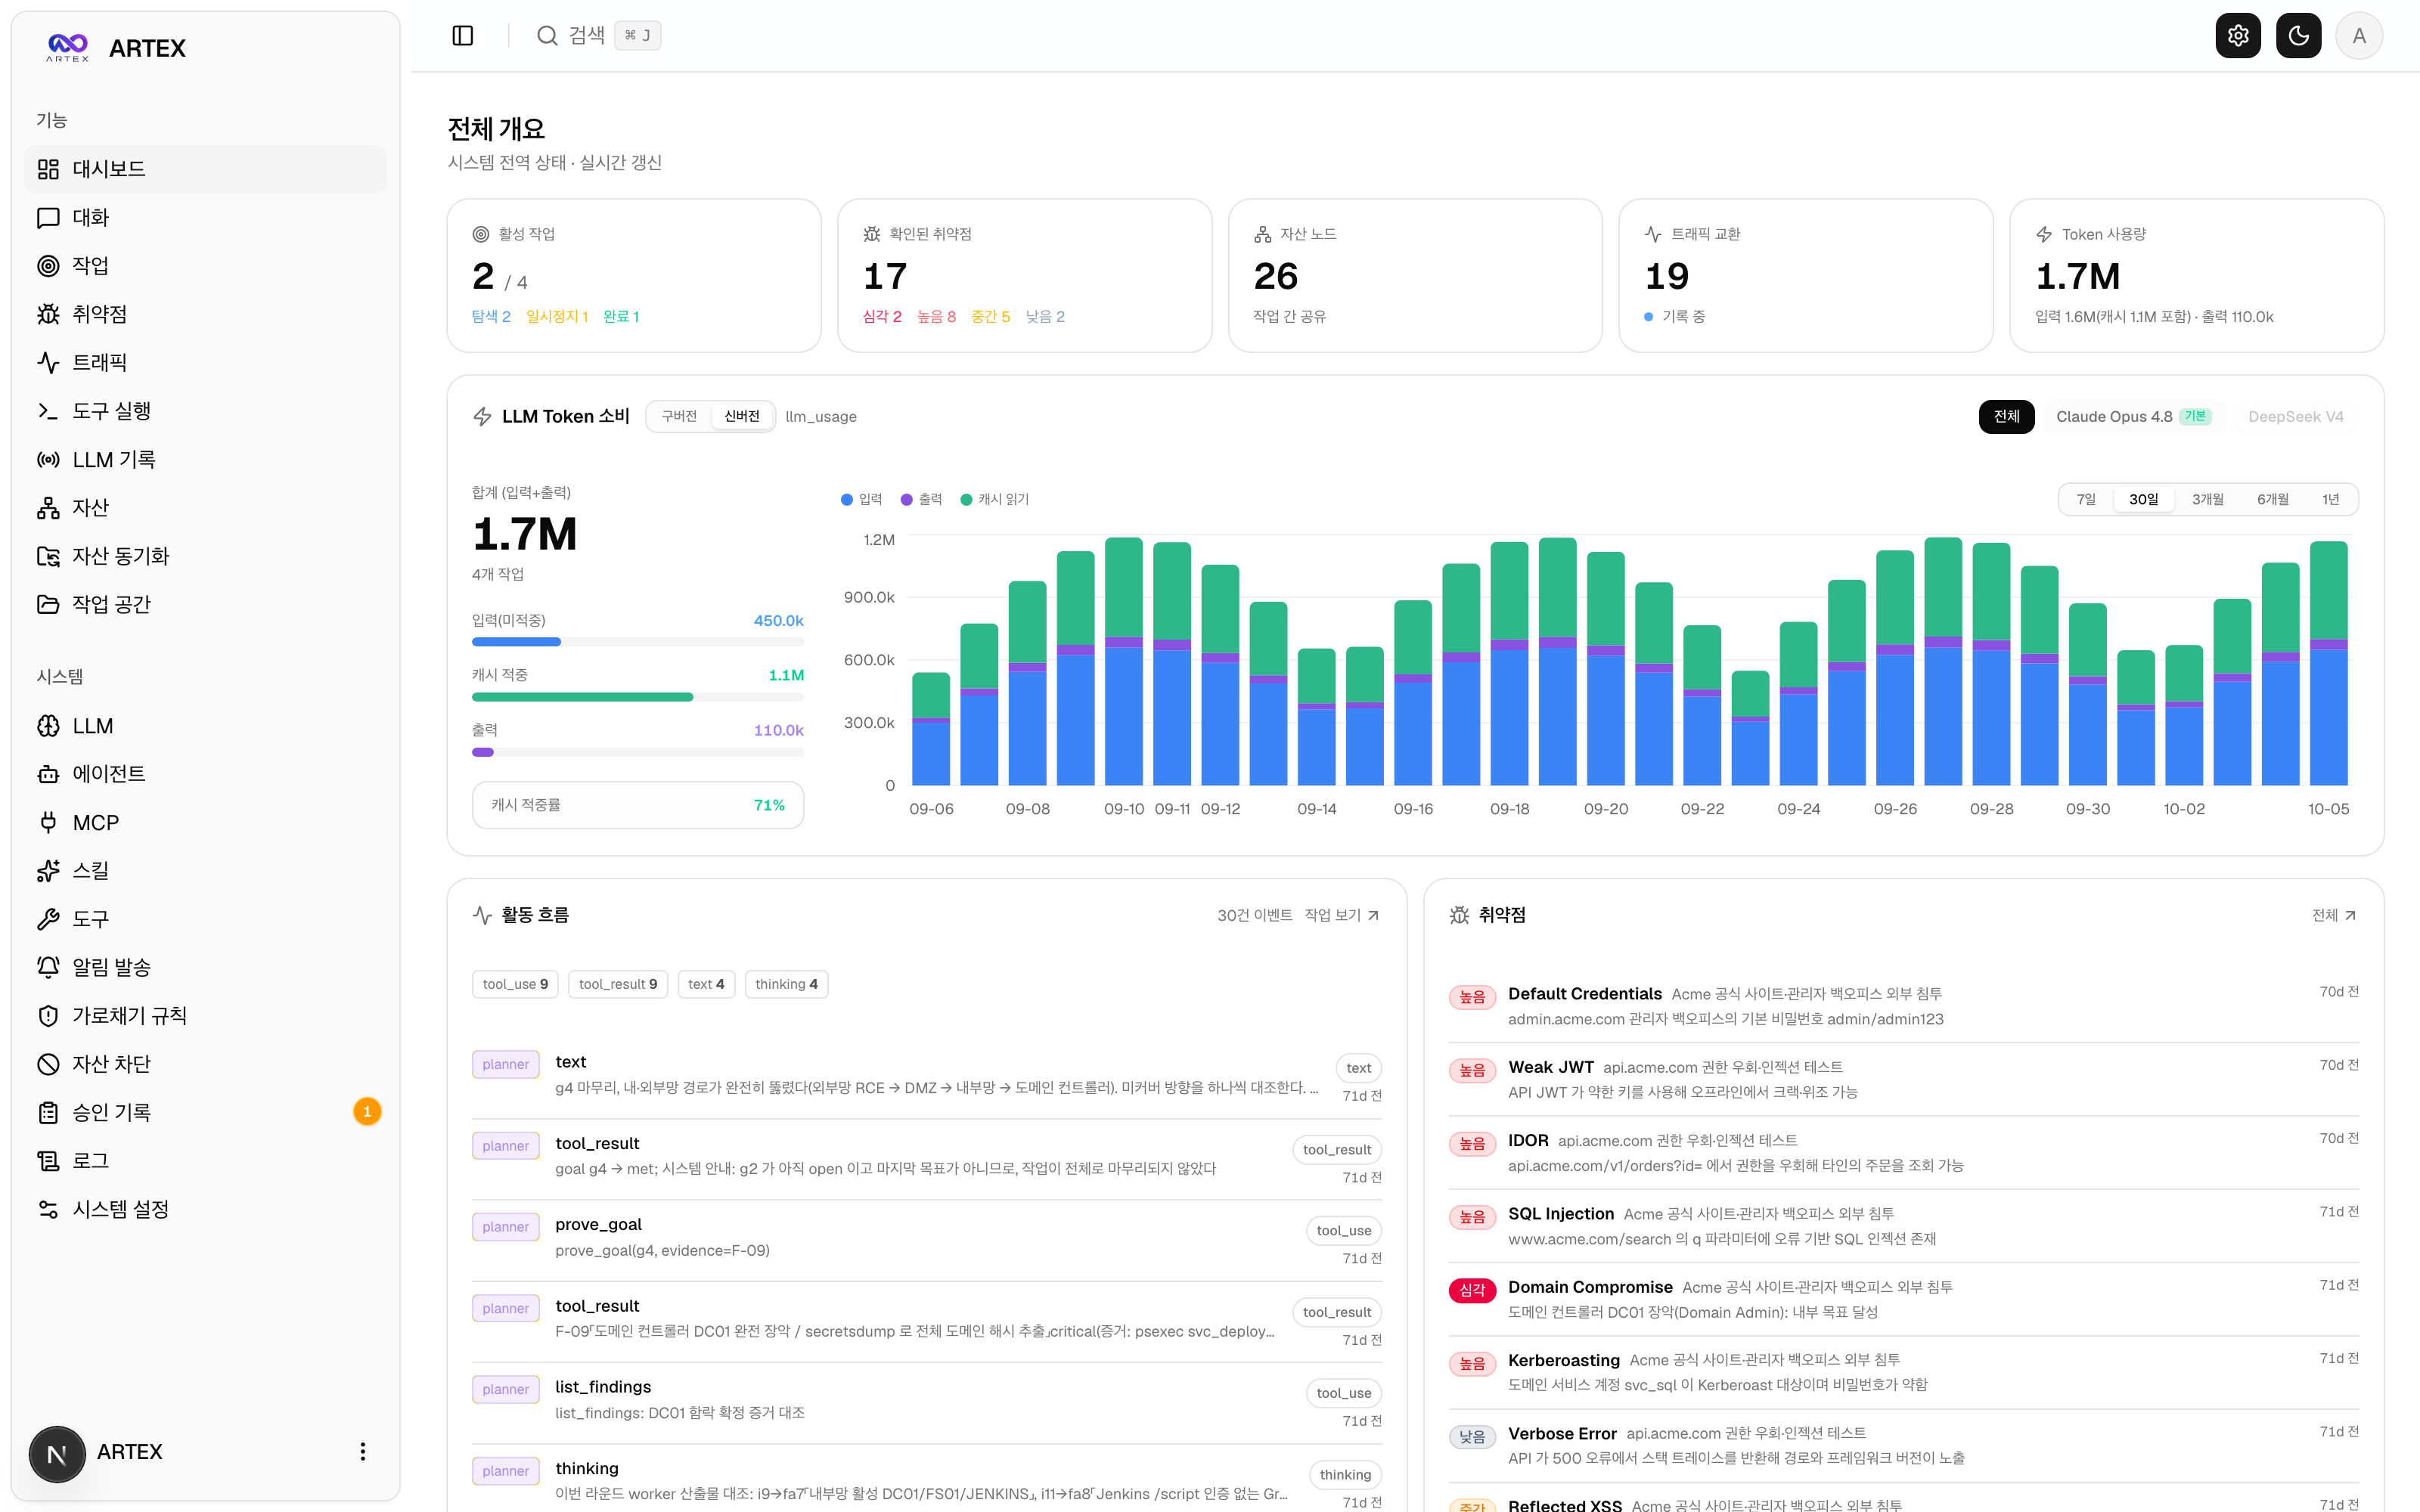
이 프로젝트는 중국산 오픈소스 ARTEX를 로컬 환경에서 쓸 수 있도록 한국어로 현지화한 배포판입니다. Go 백엔드와 Next.js 프런트엔드로 구성되며, LLM 에이전트가 타겟 시스템을 스스로 정찰하고 취약점을 탐지하여 리포트까지 작성합니다. 내부 추론 프롬프트는 원본의 성능을 유지하되 사용자 인터페이스와 결과 산출물만 한국어로 출력합니다.

보안 연구를 위해 자율 AI 공격의 작동 원리를 파악하려는 개발자에게는 유용한 학습 도구입니다. 다만 원본 프로젝트의 이미지 배포가 중단된 상태라 현재는 소스 컴파일 과정을 거쳐야 하며, 허가되지 않은 시스템에 사용할 경우 법적 책임이 따르므로 반드시 격리된 로컬 환경에서만 다뤄야 합니다.

more: https://github.com/jiwoochris/artex-ko


0sec-labs CLI and MCP server for security workflows

1 10 2026
0sec-labs CLI and MCP server for security workflows

0sec-labs is a tool for running automated security assessments and research workflows across terminal, browser, and AI coding agents. It supports Apple Silicon and Linux, offering twelve built-in templates for scanning repositories, dependencies, and native code. The software functions as a local execution runner that integrates with existing stacks via an MCP server.

If you are managing your own security infrastructure and want to script routine audits, this provides a clean interface for handling repeatable tasks. It remains a research preview and requires manual configuration of model providers to function. Avoid this if you are looking for a hands-off, out-of-the-box solution, as it demands active management of execution profiles and scope boundaries.

more: https://github.com/0sec-labs/0


Knife static binary analysis CLI in Rust

23 09 2026
Knife static binary analysis CLI in Rust

Knife is a standalone Rust CLI for static binary analysis of PE, ELF, and Mach-O files. It combines header parsing, strings extraction, and disassembly into a single tool that recovers functions from stripped binaries using exception directories. The audit command specifically flags dangerous call sites where argument provenance suggests potential bugs like integer underflows.

This is a solid alternative to juggling five separate tools if you need to triage untrusted binaries quickly. However, it is strictly static and will not help with dynamic debugging or network traffic analysis. The analysis depth depends on the quality of the binary's metadata, so heavily obfuscated or packed targets may not yield much insight.

more: https://github.com/bl4ckr0ss3/knife

my other side: ivo.blogspot.com


Pentest Harness for AI Security Testing

23 09 2026
Pentest Harness for AI Security Testing

This is a dark-mode web UI for running authorized penetration tests with multiple LLM providers. It uses a plugin architecture to manage shell access, web research, and durable session states. You bring your own API keys for any OpenAI-compatible model.

The setup is straightforward if you have Node 20 and pnpm installed. It requires explicit authorization for every engagement, so it is not for casual curiosity. The interface is dense and assumes you know what you are doing.

more: https://github.com/S1N6H/pentest-harness

my other side: ivo.blogspot.com


AgentSafe Proxy Enforces Decionis Authorization

22 09 2026
AgentSafe Proxy Enforces Decionis Authorization

AgentSafe is a lightweight HTTP proxy (v0.2.0) that you can install via Homebrew, Docker, or Helm. It intercepts each request from an AI agent or service, forwards the intent to the Decionis control plane, and only forwards the request onward when Decionis returns an ALLOW grant. The proxy records every decision as a signed dossier and never makes its own policy decisions.

If you need a clear authority boundary for autonomous agents, AgentSafe gives you a reproducible test harness and a single‑use grant model. It depends on a running Decionis service (and optionally the Presence layer) and only works for HTTP traffic, so it isn’t a drop‑in for non‑HTTP workloads or environments without those services.

more: https://github.com/decionis/agent-safe-pipeline

my other side: ivo.blogspot.com


Cybermes CLI and MCP Server

22 09 2026
Cybermes CLI and MCP Server

Cybermes is a Go‑based offensive security framework released on GitHub (v0.9.1) that bundles more than 200 modular playbooks and a native Model Context Protocol (MCP) server. It can be run as a standalone CLI for headless CI pipelines or as an MCP service that streams security tools into AI‑assisted IDEs such as Gemini, Claude, and Cursor. The package includes Docker support, Windows PowerShell installers, and a health‑check script that validates dependencies and API keys. It aims to replace ad‑hoc script collections and manual tool chaining with a single, versioned pipeline.

If you already have a mature suite of custom scripts, Cybermes adds little beyond convenience and may feel heavyweight for small bug‑bounty jobs. The MCP integration works only with supported AI clients, so environments without those assistants get only the CLI path. It’s a solid time‑saver for teams that need repeatable, AI‑augmented assessments, but not essential for solo developers who prefer direct tool control.

more: https://github.com/Zyrexnn/Cybermes

my other side: ivo.blogspot.com


How a script weakness in Mail.com’s password reset page cost Partap Davis $3000

5 03 2015

The Verge has posted an article of Partap Davis who lost his money being hacked overnight.

While he slept, an attacker undid every online security protection he set up. By the time he woke up, most of his online life had been compromised: two email accounts, his phone, his Twitter, his two-factor authenticator, and most importantly, his bitcoin wallets.

All of those accounts got hacked primarily because his main email address in mail.com was taken by the online perpetrator.

For simplicity’s sake, we’ll call her Eve.

How did Eve get in? We can’t say for sure, but it’s likely that she used a script to target a weakness in Mail.com’s password reset page. We know such a script existed. For months, users on the site Hackforum had been selling access to a script that reset specific account passwords on Mail.com. It was an old exploit by the time Davis was targeted, and the going rate was $5 per account. It’s unclear how the exploit worked and whether it has been closed in the months since, but it did exactly what Eve needed. Without any authentication, she was able to reset Davis’ password to a string of characters that only she knew.

Read the full article here:
http://www.theverge.com/a/anatomy-of-a-hack

my other side: ivo.blogspot.com


iOS7 Lockscreen Bypass

20 09 2013

Forbes’ Andy Greenberg wrote an article on the way someone bypass iPhone’s Lockscreen. Here’s the excerpt :


As the video shows, anyone can exploit the bug by swiping up on the lockscreen to access the phone’s “control center,” and then opening the alarm clock. Holding the phone’s sleep button brings up the option to power it off with a swipe. Instead, the intruder can tap “cancel” and double click the home button to enter the phone’s multitasking screen. That offers access to its camera and stored photos, along with the ability to share those photos from the user’s accounts, essentially allowing anyone who grabs the phone to hijack the user’s email, Twitter, Facebook, or Flickr account.

Read more :
http://www.forbes.com/sites/andygreenberg/2013/09/19/ios-7-bug-lets-anyone-bypass-iphones-lockscreen-to-hijack-photos-email-or-twitter/

my other side: ivo.blogspot.com


The Subway $3mio Hack

23 12 2011

Quote:

some of the franchisees “directly and blatantly disregarded” Subway’s security and POS configuration standards. “It’s not like they had to install something and they didn’t,” Schuman told Ars. “They did it proactively,” he said, downloading low-cost remote desktop software from the Internet and refusing to use point-to-point encryption as Subway dictated.

Read the full article here:
How hackers gave Subway a $3 million lesson in point-of-sale security

my other side: ivo.blogspot.com